

The XRP Ledger has activated a protocol amendment called fixCleanup3_4_0 to address a permission-related vulnerability that could allow accounts authorised to burn tokens to create new ones under specific circumstances. The flaw affected delegated PaymentBurn transactions involving issued assets, including stablecoins and other tokens. The patch prevents transactions from crossing a zero-balance boundary. XRP itself was not affected, and there have been no reported cases of the vulnerability being exploited.
More in Gadgets
Lumio Adds YouTube Shorts Feed to TLDR With New Flix Feature
November 6, 2026
Hackers Exploited Chrome and Qualcomm Vulnerabilities to Target Android Devices: Report
November 6, 2026
Want to Buy Digital Gold This Dhanteras? Here Are 5 Apps to Try
November 6, 2026
Zomato Rolls Out Limitless Delivery in Delhi NCR, Mumbai, Kolkata, More Indian Cities
November 5, 2026
WhatsApp for Android Could Soon Let You Preview Chats Without Opening Them
November 5, 2026
Motorola Signature 27 Launched With Snapdragon 8 Elite Extreme Gen 6 Chipset: Price, Specifications
November 5, 2026
Latest News
 அமெரிக்க இடைக்காலத் தேர்தல் முடிவுகள் உலகின் பிற பகுதிகளில் ஏற்படுத்தக் கூடிய தாக்கம் என்ன?
November 6, 2026
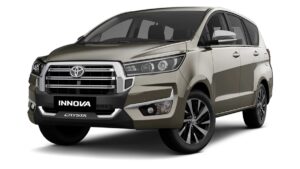 டொயோட்டா இன்னோவா கிரிஸ்டா விலை கணிசமாக உயர்வு! புதிய வேரியண்ட் வாரியான விலை பட்டியல் இதோ!
November 6, 2026
 லாஸ் ஏஞ்சலிஸ் மேயர் தேர்தலில் கேரன் பாஸை வீழ்த்தி இந்திய குடியேறி நித்யா ராமன் வெற்றி
November 6, 2026
 மொத்த சாம்ராஜ்யம் மிரளுது.. 200MP கேமரா.. 90W சார்ஜிங்.. 7000mAh பேட்டரி.. AMOLED டிஸ்பிளே.. எந்த மாடல்?
November 6, 2026
 சிலருக்கு மட்டும் ஏன் நான்கு மணிநேர தூக்கமே போதுமானதாக இருக்கிறது?
November 6, 2026
 Iran’s security chief meets Putin, delivers message from Khamenei
November 6, 2026